Brian Caswell schreibt fesselnde Erzählungen, die sich mit den emotionalen Landschaften junger Leser auseinandersetzen. Sein Schreiben zeichnet sich durch fesselndes Storytelling und die Erforschung komplexer Gefühle aus, die jugendliche Erfahrungen prägen. Caswell zielt darauf ab, die Essenz des Erwachsenwerdens einzufangen, und seine unverwechselbare Stimme macht seine Bücher zu einer unvergesslichen Reise für diejenigen, die diese prägenden Jahre durchlaufen. Tauchen Sie ein in seine Welten und entdecken Sie neue Perspektiven.
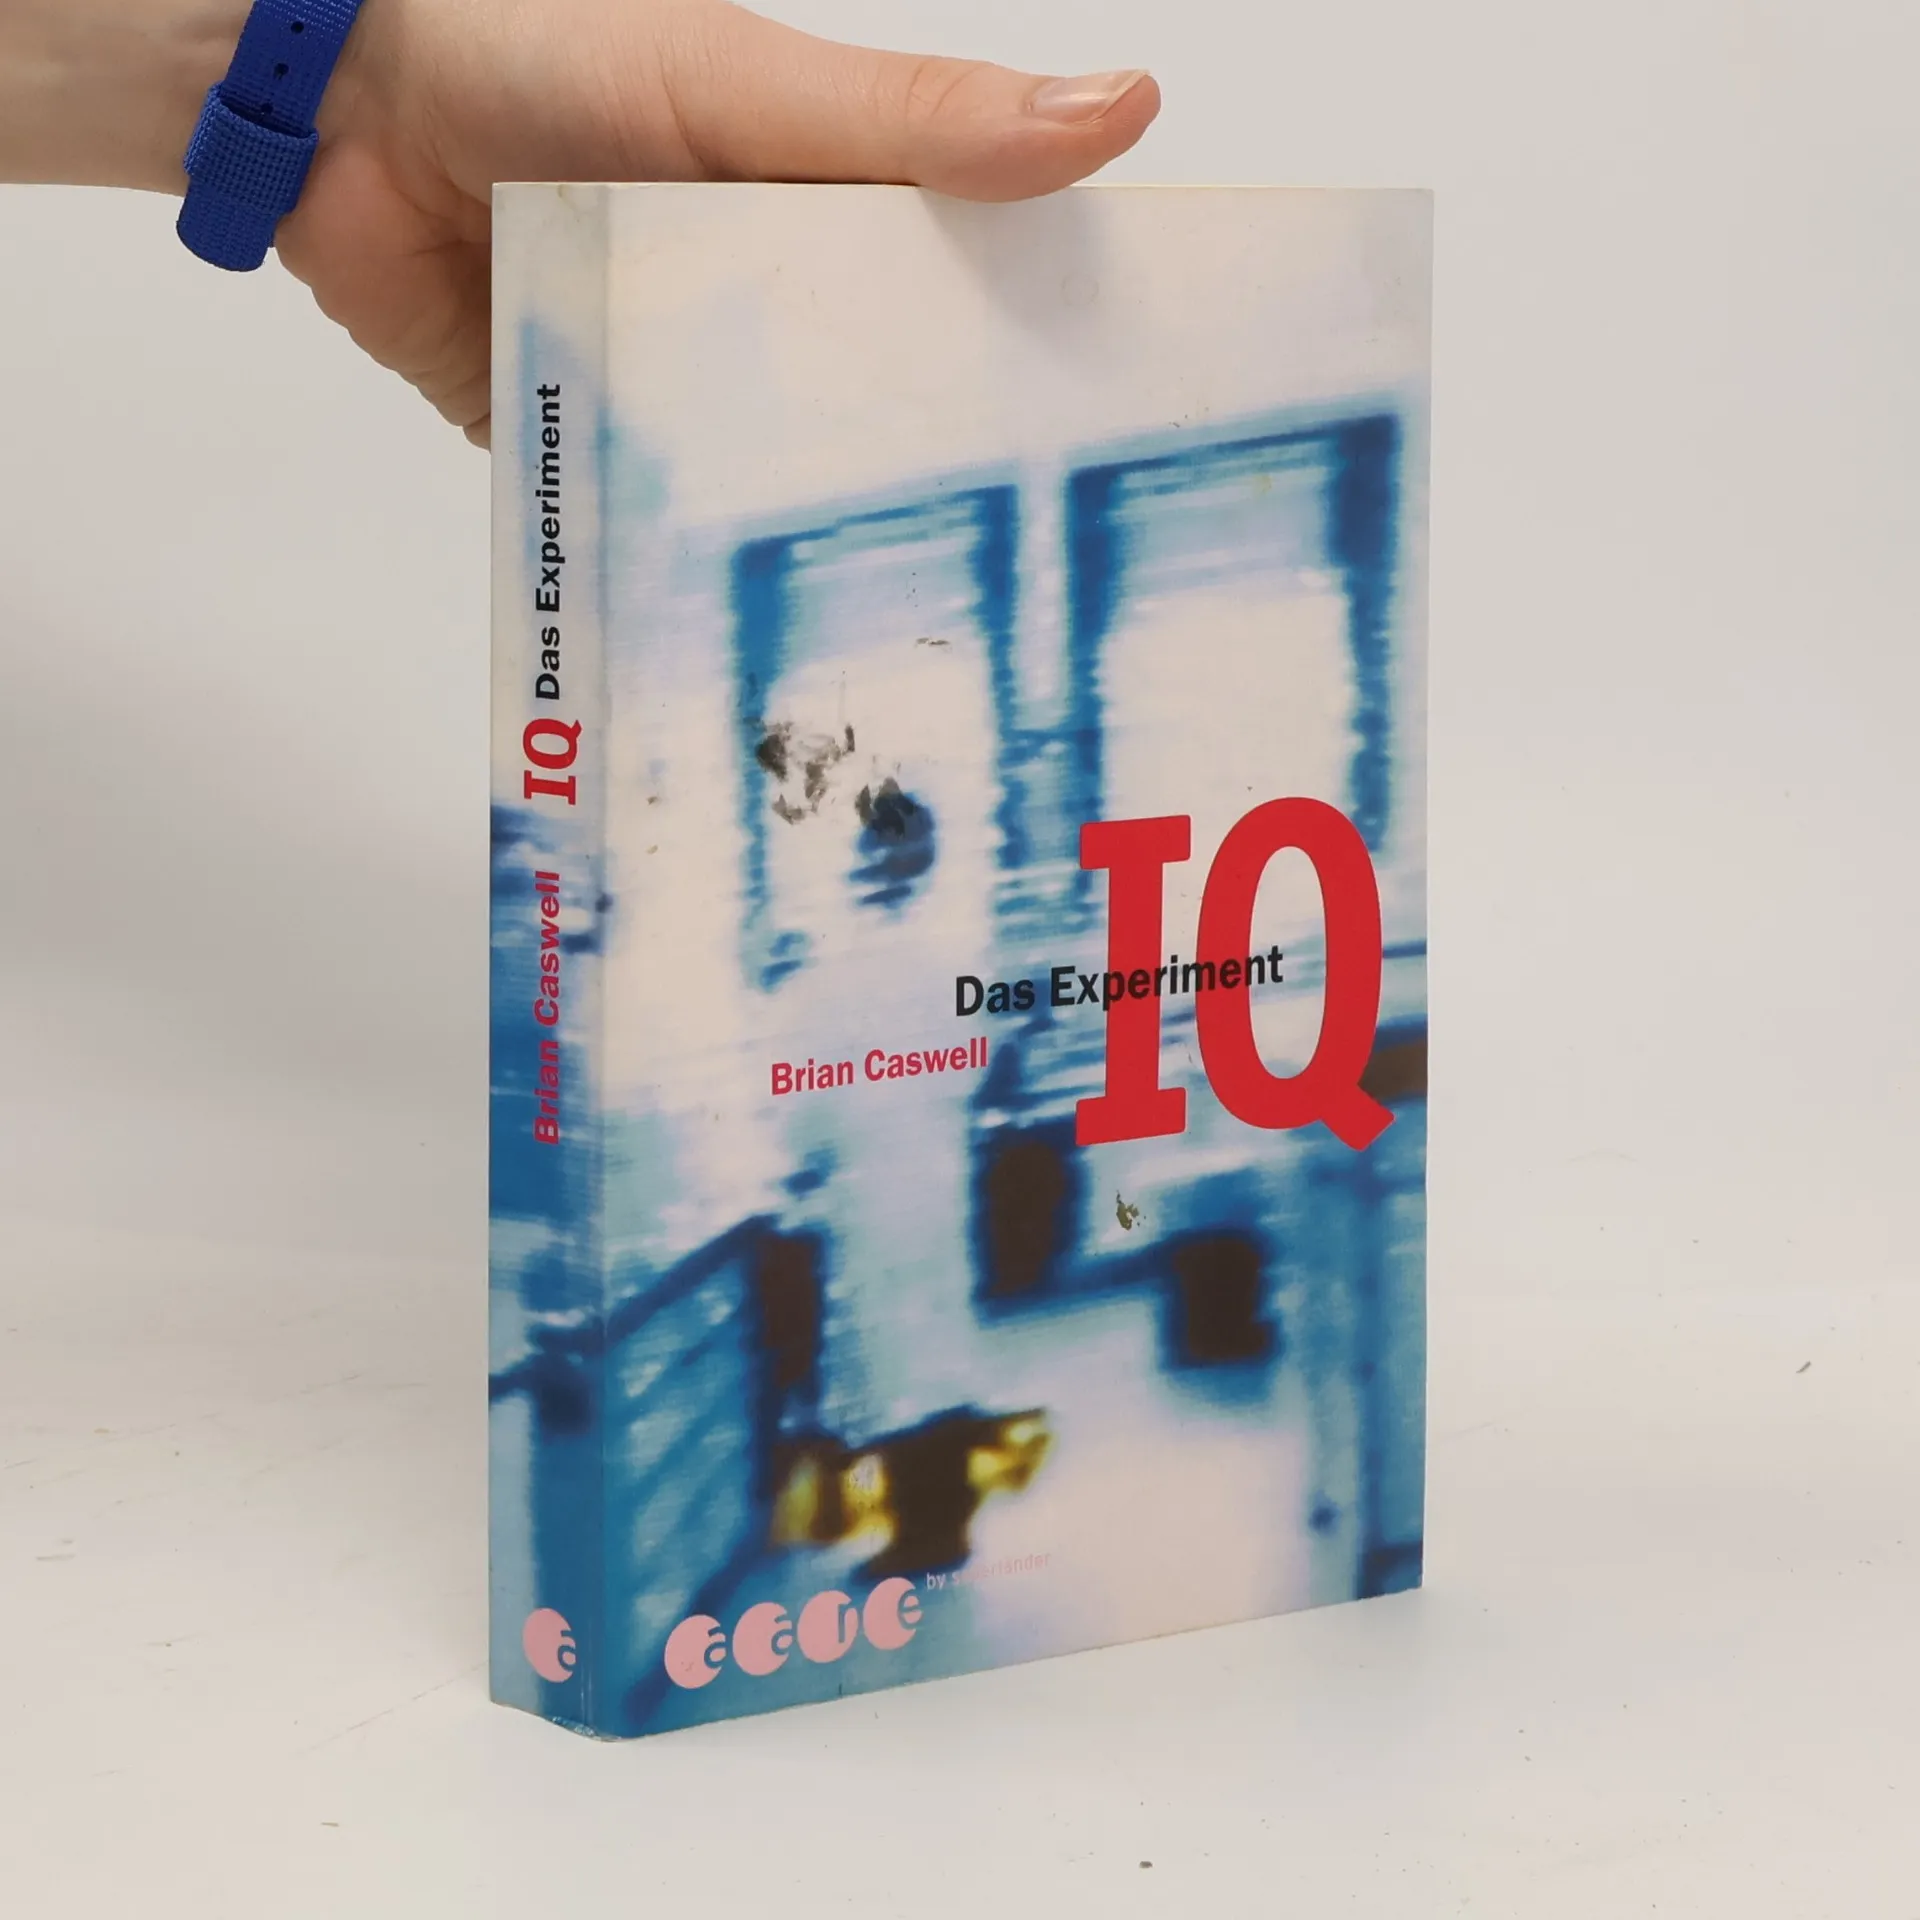
Die 15-jährige Mikki lebt zusammen mit anderen Jugendlichen auf "der Farm", einer Art Schule mit hohem IQ. Aber warum legen die undurchsichtigen Wissenschaftler Larsen und MacIntyre so großen Wert darauf, sie von der Umwelt abzuschirmen? ..
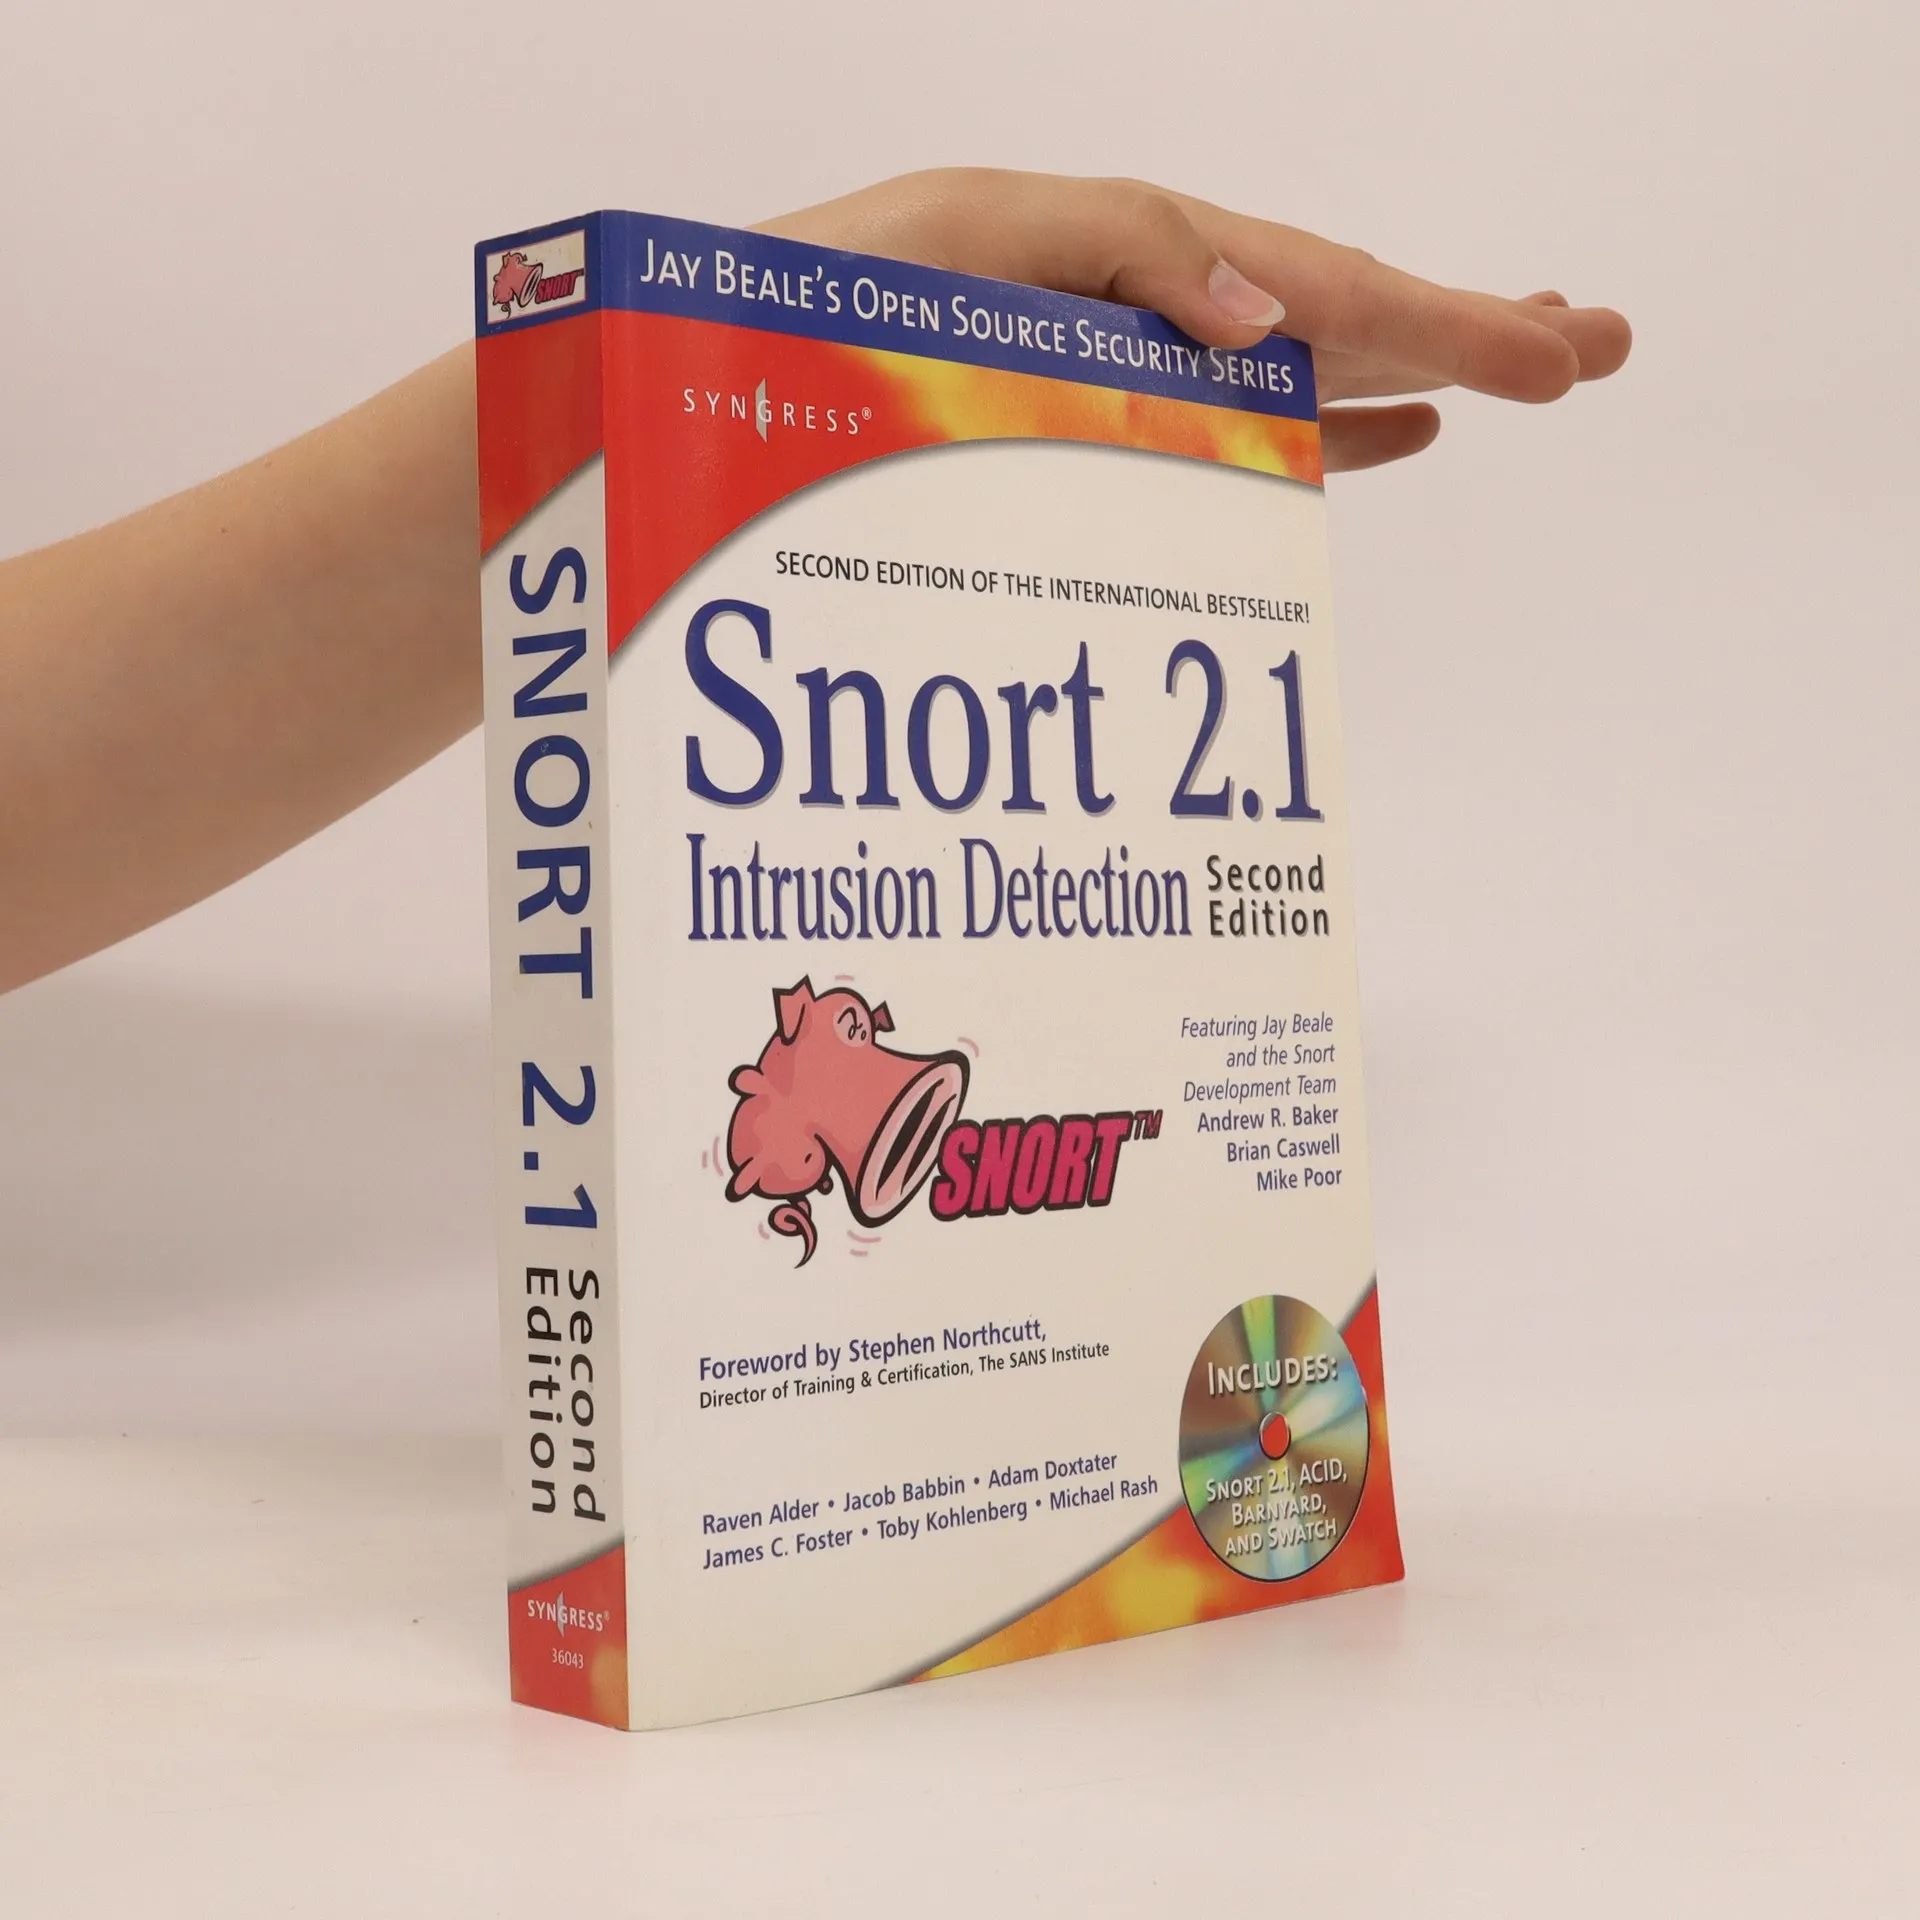
The Barnes & Noble ReviewWhy spend thousands of dollars on a commercial IDS when there s Snort? Now Snort.org webmaster Brian Caswell shows how to make the most of it -- including the latest 2.1 upgrades. Caswell covers the entire Snort planning, deployment, and management lifecycle. Integrating Snort into your security architecture. Using it as a packet sniffer and packet logger for network traffic debugging. Using and updating rules. Using Barnyard to manage Snort s output. Analyzing intrusions. Evaluating (and possibly implementing) active response. A nice touch: notes from the underground that reveal how crackers attack IDS systems, and what you can do about it. You could download those. But you re unlikely to find Caswell s depth of knowledge anywhere else. Bill CamardaBill Camarda is a consultant, writer, and web/multimedia content developer. His 15 books include Special Edition Using Word 2003 and Upgrading & Fixing Networks for Dummies, Second Edition.
Why spend tens of thousands on an Intrusion Detection System? Snort is a powerful Network Intrusion Detection System that can provide enterprise wide sensors to protect your computer assets from both internal and external attack. Snort can put the information you need at your fingertips about any suspicious activity on your network. Snort is a lightweight network intrusion detection system, capable of performing real-time traffic analysis and packet logging on IP networks. It can perform protocol analysis, content searching/matching and can be used to detect a variety of attacks and probes, such as buffer overflows, stealth port scans, CGI attacks, SMB probes, OS fingerprinting attempts, and much more.The incredible low maintenance costs of Snort combined with it's powerful security features are making Snort one of the fastest growing IDSs within corporate IT departments.